Showing posts with label Security. Show all posts

Thursday, August 20, 2015

Advanced Cyberforensics Education Consortium Webinar


Advanced Cyberforensics Education Consortium

will discuss CYBERFORENSICS

Friday, August 28th at 11 a.m. EDT.


Learn about the hundreds of online instructional videos, four course Digital Forensics sequence and more resources that are available to make your life easier!

Register TODAY for this FREE webinar.


Questions? Contact info@nationalcyberwatch.org.

National Cyber League (NCL) Registration is Now Open!


Bigger, bolder and better than EVER...

the new NCL gaming system is now powered by Cyber Skyline.

Register for National Cyber League TODAY!


Questions? 

Thursday, August 13, 2015

National Cyber League (NCL) Registration Opens Saturday, August 15th


Get psyched to become 
Cyber Superheros...


NCL registration opens this Saturday, August 15th
Bigger, bolder and better then EVER...
the new NCL gaming system is now powered by Cyber Skyline!

Learn more about NCL
CLICK HERE

info@nationalcyberleague.org

Thursday, July 30, 2015

CyberWatch West Invitation


CyberWatch West would like to invite all MPICT member institutions to join our center. 

CyberWatch West is a regional center for Cybersecurity education covering 14 states in the western US. We are heavily involved in many of the same initiatives as MPICT, including advocating for an ICT transfer model curriculum and continuing support for the ICT winter conference in CA.
Member benefits include travel sponsorships and training and there is no cost to join. For more information, please go to http://cyberwatchwest.org.

To see our member map and to apply for membership, go here: http://cyberwatchwest.org/index.php/about-us/member-map.


For additional information, please contact Corrinne Sande (PI for CyberWatch West) at csande@whatcom.ctc.edu.

Thursday, July 23, 2015

Cybersecurity Competition Federation: The Cyberfed Show


Cybersecurity Competition Federation
(CyberFed)

closes the gap among the SILOS of cybersecurity competitions by bringing unity and illuminating the pathways into the career of cybersecurity.

Click here to learn more!


The CyberFed Show highlights various cybersecurity competitions.

By subscribing, you will get a weekly birds-eye view into various competitions across the world.

To subscribe to The CyberFed Show

CLICK HERE

www.cyberfed.org

Wednesday, July 22, 2015

BBC: Car hack uses digital-radio broadcasts to seize control


By Chris Vallance BBC Radio 4

BBC

Car infotainment systems can allow drivers to see vehicle status updates, play music and videos, view maps and in some cases run third-party apps
Several car infotainment systems are vulnerable to a hack attack that could potentially put lives at risk, a leading security company has said.
NCC Group said the exploit could be used to seize control of a vehicle's brakes and other critical systems.

The Manchester-based company told the BBC it had found a way to carry out the attacks by sending data via digital audio broadcasting (DAB) radio signals.

It coincides with news of a similar flaw discovered by two US researchers.

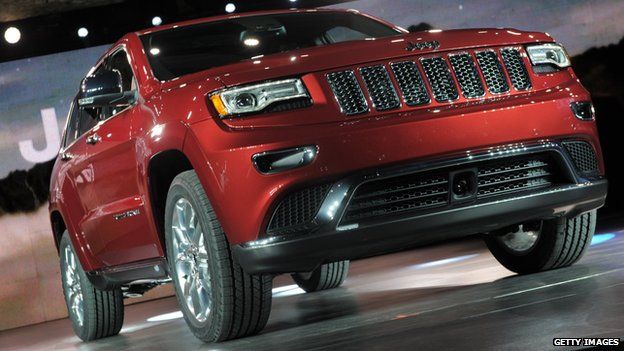
Chris Valasek and Charlie Miller showed Wired magazine that they could take control of a Jeep Cherokee car by sending data to its internet-connected entertainment and navigation system via a mobile-phone network.

Chrysler has released a patch to address the problem.

However, NCC's work - which has been restricted to its labs - points to a wider problem.

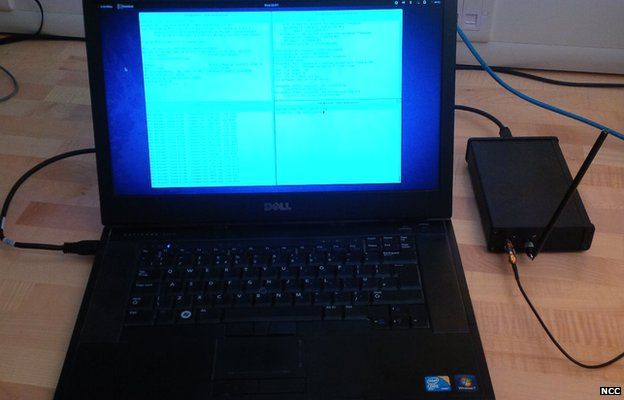
NCC Group was able to transmit the DAB signal using a laptop and a box made from easy-to-source parts
The UK's Society of Motor Manufacturers and Traders has responded by saying that car companies "invest billions of pounds to keep vehicles secure as possible".
Breached brakes
NCC demonstrated its technique to BBC Radio 4's PM programme at its offices in Cheltenham.

By using relatively cheap off-the-shelf components connected to a laptop, the company's research director, Andy Davis, created a DAB station.

Because infotainment systems processed DAB data to display text and pictures on car dashboard screens, he said, an attacker could send code that would let them take over the system.

Once an infotainment system had been compromised, he said, an attacker could use it as a way to control more critical systems, including steering and braking.

Depending on the power of the transmitter, he said, a DAB broadcast could allow attackers to affect many cars at once.

"As this is a broadcast medium, if you had a vulnerability within a certain infotainment system in a certain manufacturer's vehicle, by sending one stream of data, you could attack many cars simultaneously," he said.

"[An attacker] would probably choose a common radio station to broadcast over the top of to make sure they reached the maximum number of target vehicles."

Mr Davis declined to publicly identify which specific infotainment systems he had hacked, at this point.
Lab simulation
In many ways, modern cars are computer networks on wheels.

Mike Parris, of SBD, another company that specialises in vehicle security, said modern cars typically contained 50 interlinked computers running more than 50 million lines of code.

By contrast, he said, a modern airliner "has around 14 million lines of code".

The addition of automated car controls are creating new opportunities for hackers
Such technology allows the latest cars to carry out automatic manoeuvres. For example, a driver can make their vehicle parallel park at the touch of a button.

Mr Davis said he had simulated his DAB-based attack only on equipment in his company's buildings because it would be illegal and unsafe to do so in the outside world.

But he added that he had previously compromised a real vehicle's automatic-braking system - designed to prevent it crashing into the car in front - by modifying an infotainment system, and he believed this could be replicated via a DAB broadcast.

"If someone were able to compromise the infotainment system, because of the architecture of its vehicle network, they would in some cases be able to disable the automatic braking functionality," he said.
Jeep attack
On Tuesday, Wired magazine reported that two US security researchers had managed to remotely take control of a Jeep Cherokee's air-conditioning system, radio and windshield wipers while its journalist was driving the vehicle.

Wired magazine reported that a Jeep Cherokee had been hacked
Mr Valasek - director of vehicle security research at IOActive - said that NCC's attack appeared to have similarities with his own.

"I mean that's essentially what we did over the cell [mobile] network - we took over the infotainment system and from there reprogrammed certain pieces of the vehicle so we could send control commands," he said.

"So, it sounds entirely plausible."

But he added that such exploits were beyond the reach of most criminals.

"It takes a lot of time skill and money," he said.

"That isn't to say that there aren't large organisations interested in it."

More details about both the NCC and the US team's research will be presented to the Black Hat security convention in Las Vegas next month.

CSSIA Faculty Training Registration will be Closing SOON...


Don't delay, REGISTER today!
Upcoming Trainings
  • SCADA 
  • Netlabs+ User Community Workshop 
  • (ISC) CISSP Course 
  • EMC's Coud Infastructure & Services v2 (CIS) 
  • Essentials 1 & 2: Firewall Installation, Configuration and Management 
  • EMC's Information Storage & Management v2 (ISM) 
TO REGISTER,


http://www.cssia.org/cssia-training.cfm


For questions regarding trainings,

contact Lynn Dohm at lynn.dohm@morainevalley.edu.


www.cssia.org

The National Resource Center for Systems Security and Information Assurance (CSSIA) | lynn.dohm@morainevalley.edu | 9000 W. College Parkway | Palos Hills, IL 60451 United States

Tuesday, July 21, 2015

CyberCalifornia Launch


As we have seen in recent news headlines, security breaches can bring entire organizations, states and countries to their knees. In today's connected world, making security a top priority is no longer a choice - it's a must. As public and private organizations continue to operate within this new era of the Internet, security will become critical to maintaining trust with the public, building company reputation, as well as safeguarding data, IP and critical infrastructure.

California is at the center of the digital revolution that is shaping the world around us. Already a national center of commercial cybersecurity activities, California is home to companies building the cybersecurity products and solutions that are securing commercial businesses, academic institutions and governmental organizations across the globe.

In an effort to help advance the goals and promote the accomplishments of the Governor's Cybersecurity Task Force, CyberTECH, among other state and local leaders, recently launch CyberCalifornia.


CyberCalifornia will organize public-private partnerships in cybersecurity, with the goals of facilitating research and innovation in cybersecurity, educating California businesses about cybersecurity needs and resources, and connecting California's robust workforce development system with the needs of California employers.

Led by its Board of Advisors, CyberCalifornia activities include:
Assisting in the organization of private sector advisory groups by vertical industry such as banking and finance, high technology, agriculture, etc.
Assisting in the development and promotion of cybersecurity career pathways
Partnering with local and regional economic development organizations to inform California's small business community about cybersecurity needs and solutions
Establishing connections between the cybersecurity and Internet of Things sectors through activities such as conferences and media events

To learn more about CyberCalifornia, please contact darin@cyberhivesandiego.org.


Darin Andersen, CEO, CyberUnited, Co-Chair, CyberTECH, Co-Chair, Economic Development Subcommittee, California Cybersecurity Task Force

"CyberCalifornia: Cybersecurity and IoT Gold Rush"

Recently, CyberTECH helped launch CyberCalifornia with other State and local leaders. The initiative is organized in conjunction with the Innovative Hub (iHub) Network, a program administered by the State Office of Economic Development and in partnership with Governor Brown's Cybersecurity Task Force.


Jerry Brown, Governor of California

CyberCalifornia will organize public-private partnerships in cybersecurity to better protect California's critical infrastructure, businesses and citizens from cyber threats, facilitate research and innovation in cybersecurity, educate California businesses about cybersecurity needs and resources, and connect California's robust workforce development system with the needs of California employers.

Center of Cybersecurity and Internet of Things Excellence (CCIoTE)
California is home to the personal computer, the firewall, anti-virus and many other cybersecurity products. Today, California companies are at the forefront of new technologies ushering in the Internet of Things (IoT), the term for the phenomenon where people and things are connected to the Internet, leveraging sensors and real time analytics and cloud technologies.

California's leadership role in advanced technology sectors including autonomous vehicles, biotechnology, precision in medicine and advanced manufacturing, will contribute to the State's continued excellence in cybersecurity and privacy. The powerful combination of cyber and the emergence of these innovative intensive sectors make California the perfect place to build secure next generation technologies.

California has a rapidly growing information technology industry cluster and offers the full spectrum of cybersecurity capabilities. Our Golden State has tremendous assets to keep our Country safe, advance innovation with security and privacy built in and be a beacon for other States in our Nation to follow.


Charles "Chuck" Brooks, Vice President, Government Relations and Marketing, Sutherland Global Services

"Adopting a Cooperative Global Cyber Security Framework to Mitigate Cyber Threats (Before it is too Late)"
The recent OPM cyber breach at the U.S. Government's Office of Personnel Management (OPM) provided a wakeup call to the seriousness and sophistication of the cyber security threat aimed at both the public and private sectors. The fact is that over 43% of companies had breaches last year (including mega companies such as Home Depot, JPMorgan, and Target). Moreover, the intrusion threats are not diminishing. For example, British Petroleum (BP) faces 50,000 attempts at cyber intrusion every day.

According to the think tank Center for Strategic and International Studies (CSIS), cyber related crime now costs the global economy about $445 billion every year. These cyber security breaches demonstrate that there is a continued need for protocols and enhanced collaboration between government and industry.

In 2014 code vulnerabilities such as Heartbleed, Shellshock, Wirelurker, POODLE and other open source repositories caused chaos and harm. The cyber security community responded to those vulnerabilities with "react and patch." Unfortunately, this means of response has been for the most part, a cosmetic or band aid approach.

The cyber security community's posture must change to one of wait and react to that of being proactive and holistic. It is not really a question of which policies, processes and technologies are ready and best, that will always be debatable. Being proactive means adopting a working Industry and Government Global Cyber Security Framework that would include measures for encryption, authentication, biometrics, analytics, automated network security, and a whole host of other topics related to cyber threats.

CONTINUE READING


LIFARS, Featured CyberTECH Member

LIFARS is a digital forensics and cybersecurity intelligence firm based in New York City. With its history of investigating cybersecurity breaches across a number of industries, LIFARS is uniquely positioned to help increase cybersecurity posture to protect organizations and individuals from real-life hackers and advanced persistent threat actors. By bringing in LIFARS, you can maximize your existing investment into the cybersecurity infrastructure and make sure that your future investments are strategically placed – delivering maximum protection while preserving the productivity of your employees. For these and other reasons, LIFARS was recently ranked as the #2 cybersecurity company in New York Metro area on the Cybersecurity 500 list.

LIFARS WEBSITE

In addition to providing robust security solutions based on best practices and personal hands-on experiences, LIFARS continuously explores the latest innovations in the cybersecurity field and always seeks to find what is shaping tomorrow's industry landscape. In a recent interview with Founder and CTO of LIFARS, Ondrej Krehel, and LIFARS' Digital Forensic Examiner, Paul Kubler, they discussed strategies and policies for cybersecurity in the world today, including common mistakes and how to make them right.

LIFARS INTERVIEW


NXT Robotics is a San Diego-based company that designs and builds service robots to support the increasing needs of the hospitality industry. NXT Robotics' service robot platforms are able to provide delivery, security and guest-related services to customers - all while maintaining a consistent and high degree of quality.

The company's founder, Jeff Debrosse has over 20 years of software engineering, cybersecurity R&D and enterprise product management and deployment experience. "This is an exciting time for NXT Robotics," said Jeff. "With access to the CyberTECH community and its resources, our success is further guaranteed."

The company will be providing CyberTECH's incubator and shared workspace offices, CyberHive and iHive, with its own Nixie. "Your team, tenants and guests will find Nixie to be amazingly pleasant to deal with - not to mention, very useful!" Jeff stated.

"NXT Robotics understands the importance of making cyber part of the foundation. We are thrilled to have NXT Robotics join CyberTECH as a member and look forward to working closely with Jeff and his team." said CyberTECH Co-Chair and Founder, Darin Andersen.

We are proud to recognize NXT Robotics as a featured CyberTECH Member for July 2015.


NXT ROBOTICS WEBSITE


Bird Rock Systems, Featured CyberTECH Member
Bird Rock Systems is a company that has been built on a foundation of exceptional customer service, technology and long-term partnership. Bird Rock Systems excels at deploying the latest enterprise class technologies including: security, routing, switching, traffic management, WAN acceleration, wireless, IP communications, storage area networking, performance computing and virtualization. Bird Rock typically begins a new client engagement by completing a network or security assessment. Their many loyal customers represent enterprise business, casino, university, Fortune 500 and government organizations requiring 'Best in Class' secure technical solutions.

BIRD ROCK SYSTEMS WEBSITE


iWebGate, Featured CyberTECH Member
Founded in Australia in 2004 with global corporate operations in North America, iWebGate has pioneered a new form of virtualization technology - the Virtualization of Network Services. iWebGate's LaunchPad allows organizations to properly and securely segment networks, connectivity and devices, eliminating the need for Firewalls and VPNs as primary security and connectivity solutions. By deploying the iWebGate Workspace Suite, organizations can then integrate security and business applications into the iWebGate LaunchPad transforming them from "enterprise friendly" products into "enterprise ready" solutions. The result is faster, more secure and reliable access to networks and network services.

IWEBGATE WEBSITE


San Diego Venture Group Selects Fhoosh as a 2015 Cool Company
Cybersecurity software development firm FHOOSH, Inc. has been chosen as a "Cool Company" by the San Diego Venture Group (SDVG) for a second year. One of 31 Cool Companies selected this year from over 160 applicants, FHOOSH continues to represent the leading edge of San Diego-area tech innovation.

FHOOSH helps corporations, institutions and government organizations protect and power valuable stored digital information with its cybersecurity platform and productivity software. FHOOSH bankLevel+ cybersecurity safeguards an organization's critical business and customer data from cyber threats by storing it in a state that is useless to hackers. It does this approximately five times faster than storing data unencrypted, with technology that breaks apart, disassociates, separately encrypts, and then disperses the data. The system also quickly notifies network administrators when unauthorized individuals try to access FHOOSH-protected databases, object stores and file systems. FHOOSH implements with existing infrastructure and allows corporate partners to dial in the security, big data/analytics and performance they need. With 15 patents pending, FHOOSH technology has been validated by the foremost cybersecurity response and assessment firm.

CONTINUE READING


Maggey Felix, Featured CyberTECH Advisor

Maggey Felix specializes in Marketing and Operations with 5+ years of experience in the technology and cybersecurity industry. Her passion for cybersecurity and cutting-edge technologies is shown through her dedication to helping companies better prepare, organize and market their solutions.

Over the past two years, Maggey has worked closely with the CyberTECH organization to support various marketing and operational activities. Her ongoing effort and commitment to CyberTECH makes Maggey an invaluable member of the community.

We are proud to recognize Maggey Felix as the featured CyberTECH Advisor for July 2015.


Julia Scholl, CyberTECH Director of Marketing and Operations

Julia Scholl is a strategic and forward-thinking public relations and marketing professional with over five years of experience working with non-profit and startup organizations. A capable self-starter with excellent organizational and communication skills, Julia is passionate about building and fostering lasting relationships within the CyberTECH community.

As Marketing and Operations Director, Julia will assist with daily operations, provide membership support as well as ongoing support with events, programs, and all other CyberTECH initiatives.

We are excited to welcome Julia to CyberTECH. Please feel free to contact Julia directly at julia@cyberhivesandiego.org.


Jessica Herrmann, CyberTECH Events Coordinator

Jessica Herrmann has over 20 years of experience applying key leadership, communication and problem solving skills within the hospitality industry. As Catering and Events Manager, Jessica has worked with a number of organizations to develop, manage and execute top quality events.

Jessica recently joined CyberTECH as Events Coordinator where she will help with the planning, organization, preparation and execution of CyberTECH events.

Please join us in formally welcoming Jessica to the CyberTECH community.

Upcoming Events
Internet of Things (IoT) Meetup - September 17, 2015

SAM Fest (Startups + Art + Music) - September 23-24, 2015

IoT Startup Table Breakfast - October 13, 2015


Check out their new brand video and you’ll see why Webpass isn’t just another ISP. They're leaders and innovators on a mission to change the way people think about the Internet. You can contact them at 1-800-Webpass!


Step Inside Webpass!
CyberTECH 2015 Newsletter Sponsor
Webpass, a leading Internet service provider in the San Diego area is now delivering residential Internet connections at 100, 200, or 500 Mbps and business Internet connections from 10-1000 Mbps. There has never been a better time to cut the cable and switch to Webpass for your Internet needs! As the owner and operator of its Ethernet network, Webpass promises customers a simple urban Internet experience. They distinguish themselves from the competition through the simplicity of set-up, absence of contracts and personable customer service.

Sign up today and instantly browse the Internet without modems, contracts or gimmicks.

Webpass
1360 5th Avenue
San Diego, CA 92101
1-800-Webpass 


Facebook


Twitter


Website


LinkedIn


Email


Instagram


Get Involved!

A key CyberTECH operating principle is collaboration. We are always looking to partner with individuals and organizations looking to get involved in various cyber and IoT initiatives throughout the region and across the globe. Opportunitites include event chair, volunteer, champion, program chair and more. For additional information on how you can support CyberTECH, please contact Julia Scholl.


Join the CyberTECH Meetup Groups
CyberTECH Cybersecurity Meetup

CyberTECH Internet of Things Meetup


Facebook


Twitter


Website


Email


LinkedIn

Our mailing address is:
1855 1st Ave. Suite 103, San Diego, CA 92101 

Monday, July 20, 2015

BBC: United hackers given million free flight miles


By Chris FoxxTechnology reporter

16 July 2015 BBC


US airline United has rewarded two hackers who spotted security holes in its website with a million free flight miles each.
The flight provider operates a "bug bounty" scheme that rewards hackers for privately disclosing security flaws rather than sharing them online.

It has given the maximum reward of a million flight miles, worth dozens of trips, to two people.

One security expert said the scheme was a big step forward for online security.

"Schemes like this reward hackers for finding and disclosing problems in the right way. That makes the internet safer for all of us," said security consultant Dr Jessica Barker.

"Bug bounties are common in tech companies as they tend to understand online security a bit more, but other industries are catching up," said Dr Barker.
Cash incentives
The idea of responsible disclosure, reporting issues and giving companies time to fix them, is not new.

Big technology companies such as Yahoo, Google and Facebook offer hackers cash incentives to report bugs privately.

In return for receiving their flight rewards, hackers are forbidden from revealing the nature of the security holes they discovered.

"We believe that this program will further bolster our security and allow us to continue to provide excellent service," United said on its website.

The company declined to comment further.

A million award miles could pay for dozens of internal flights in the US
"It's not always about hackers digging around looking for flaws. A hacker may be using a service and notice something a bit off," said Dr Barker.

"We all benefit if they look into that," she added.

Some critics of bug bounties say they can discourage companies from hiring professional security staff, because it's cheaper to offer hackers cash for disclosing bugs.

Dr Barker disagrees: "It should be part of an overall approach to security, but it's definitely a good approach.

"It encourages positive behaviour and shows young hackers that they can benefit from doing the right thing.

"Bounties can also benefit smaller companies who can't afford to give out cash rewards but can offer free products or services, so I hope we'll see more and more bug bounties," she said.

Thursday, July 16, 2015

Can Cybercompetitions Help Grow Local Security Talent?

Hiring cybersecurity staff is difficult, but federal, state and local governments are working with nonprofits to encourage the development of cybersecurity skills through individual and team competitions.
BY DAN LOHRMANN / JULY 15, 20150

Wherever I travel, the top concern on the minds of CIOs and chief information security officers is the same — everyone needs more cybersecurity talent. The problem has become especially acute in government, where it’s compounded by an improving economy, growing enterprise cyberneeds and a retiring public workforce. The bottom line:Hiring cybersecurity staff is hard for state and local governments.

What can possibly be done? If the most experienced cyberexperts are becoming too expensive, how can the public sector attract the skilled security professionals it needs?

One answer growing in popularity is to “get in the game” — literally. Across the world, various forms of cybercompetitions are growing in participation. Federal, state and local governments are working with nonprofits to encourage the development of cybersecurity skills through individual and team competitions.

Or, to use a sports analogy, if you can’t compete in the free agency market for top talent, refresh your “farm team” and grow your own talent starting at an early age.

All across the U.S., young people love to compete and not just in sports. There are many academic competitions, from university debate teams to the National Spelling Bee to high school quiz bowls.

But how do cybercompetitions fit in?

According to the U.S. Department of Homeland Security’s website oncybercareers and studies: “DHS believes hands-on cybercompetitions are a valuable learning method for all students, regardless of level. Cybercompetitions are interactive, scenario-based events or exercises that help students develop and increase cybersecurity skills outside the traditional academic environment.”

Typically teams of students work together to attack and defend against the opponent’s networks and computer systems. For example, in a cyber “capture the flag” game, players race to answer security challenges by seeking digital “flags” hidden on servers, in encrypted text or in applications. When a player or team submits a flag, they receive points for solving the challenge. The team with the highest cumulative score wins.

There are plenty of cybercompetitions geared toward different skill and age levels. A few options:

1. The Air Force Association CyberPatriot program has three main programs: the National Youth Cyber Defense Competition, AFA CyberCamps and the Elementary School Cyber Education Initiative.

2. The annual National Collegiate Cyber Defense Competition, which began in 2004, is like the March Madness of cybercompetitions. Colleges compete in state events, leading to regional and national competitions.

3. The U.S. Cyber Challenge consists of competitions, cybercamps and a virtual community to help the public and private sectors, as well as high schools and universities.

4. SANS Cyber Aces offers state competitions as well as national opportunities for individuals to compete and learn. NetWars, also from the SANS Institute, is a cybergame based on the idea that the best way to learn is via hands-on experience with real-world scenarios.

5. The National Cyber League provides ongoing virtual training for faculty and students to develop and validate cybersecurity skills using content aligned with individual and team games. This approach is used across diverse industry certifications, curricula, job roles and verticals.

6. The Michigan Cyber Range offers many chances for public- and private-sector organizations to test team skills in Alphaville, a virtual small town. They can attack and defend the city hall, utilities, library and more in various scenarios.

Cybercompetitions have become the new normal for learning and improving ethical hacking techniques and cyberdefense in a safe, fun, challenging environment. Whether you’re a middle school student just starting to learn cybersecurity concepts, an unemployed millennial who wants to switch careers, a midlevel security expert with a computer science degree or a government supervisor trying to attract the right employees, it may be time for you to join a cybercompetition.

My advice? Get in the game.
Dan Lohrmann | Contributing Writer

Daniel J. Lohrmann is an internationally recognized cybersecurity leader, technologist and author. During his distinguished career, Dan has served global organizations in the public and private sectors in a variety of executive leadership capacities, including enterprise-wide Chief Security Officer (CSO), Chief Technology Officer (CTO) and Chief Information Security Officer (CISO) roles in Michigan.

Dan Lohrmann joined Security Mentor, Inc. in August 2014, and he currently serves as the CSO and Chief Strategist for this award-winning training company. Lohrmann is leading the development and implementation of Security Mentor’s industry-leading cyber training, consulting and workshops for end users, managers and executives in the public and private sectors. Read Dan's full bio.

BBC: Darkode hacking forum forced offline

By Leo KelionTechnology desk editor  BBC

15 July 2015
From the sectionTechnology
The Darkode forum, which was created about six years ago, can no longer be accessed
Darkode - a notorious hacking forum used by Lizard Squad and other cybercriminals - has been shut down after an investigation carried out by authorities in 20 countries.
"We have dismantled a cyber-hornets' nest... which was believed by many, including the hackers themselves, to be impenetrable," said one of the US state attorneys involved.

Twenty-eight people have been arrested.

They include a 26-year-old man from Coventry, England.

In addition, the UK's National Crime Agency said an address in Paisley, Scotland, had been searched and material removed for examination. It said that five other suspected members of the site had previously been arrested.

The FBI added that dozens of other people linked to the site had been charged or had their property searched as part of the inquiry.
Restricted access
Darkode's members allegedly used the site to trade and to share hacking tools and information, including details of zero-day attacks - techniques that exploited flaws in products that neither their creators nor the wider security industry were aware of, and thus could not be protected against.

This information was password-protected.

"Only those proposed for membership by an existing user could join, but not until they posted a resume of the skills and achievements that could contribute to the criminal community," explained the NCA.

"There was a hierarchical membership structure, and the status of users determined who they could communicate with, and their access to the commodities and services on offer."

Although the site was not accessible to the general public, it was profiledextensively by the security blogger Brian Krebs, who posted several screenshots on his site.

Botnets - networks of hijacked computers used to mount co-ordinated attacks - were promoted on the site
"Most of the cybercrime forums are in Russian or some other language that's not English, but this was an English-language forum," he told the BBC.

"And it was a sort of meeting ground for cybercriminals from different nationalities and languages.

"A fairly significant number of people were selling botnet services there, and there were also services for deploying malware and phishing."

He added that the forum's visitors included members of Lizard Squad - a group of hackers which has carried out high-profile attacks on Sony, Microsoft and others.

"The guy that was most recently the admin of the forum used the nickname Sp3c," Mr Krebs recalled.

"He was a leading member of the Lizard Squad. What's interesting is that you don't see his name in the lists of those that were apprehended or charged as part of this.

"I don't really know what that means, but there was a definite connection between the Lizard Squad and this forum, at least in the last year or so."

The FBI said that Operation Shrouded Horizon had indicated up to 300 people had used the forum.

"During the investigation, the bureau focused primarily on the Darkode members responsible for developing, distributing, facilitating and supporting the most egregious and complex cybercriminal schemes targeting victims and financial systems," it said.

It added that its counterparts in Australia, Bosnia, Brazil, Israel, Colombia and Nigeria were among those involved in the international crackdown, and that efforts to trace other suspects were "ongoing".